Insider Spotlight
The CrowdStrike 2026 Legal Threat Landscape Report found that financially motivated adversaries accounted for 82 percent of observed malicious activity against the legal sector, underscoring the commercial value of sensitive legal and corporate information.
Although the report primarily examines attacks against US law firms, its findings highlight potential vulnerabilities for legal practices in Southeast Asia that handle corporate transactions, intellectual property, and confidential government communications.
Potential entry points
Law firms hold sensitive information that extends beyond their own operations, making them potential entry points for cybercriminals seeking access to businesses, financial institutions, and government organizations.
For Philippine firms advising multinational companies and handling cross-border transactions, compromised client information could expose multiple organizations to data theft and extortion.
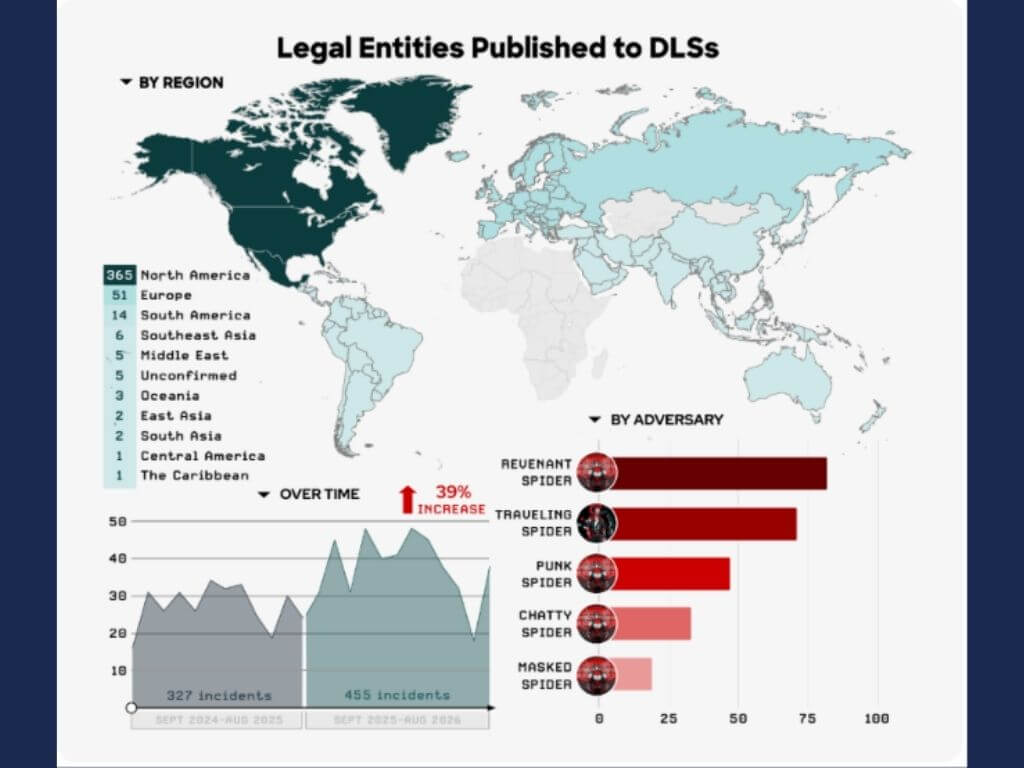
CrowdStrike reported that cybercrime group CHATTY SPIDER increased its malicious activity by 129 percent, including attempts to recruit individuals to impersonate IT personnel and physically infiltrate law offices.
‘New ATM for cybercriminals’
Cybercriminals are combining digital attacks with physical infiltration while reducing the time between gaining access and stealing information.
In one incident, attackers attempted to extract sensitive data just four minutes after obtaining initial access.
Meanwhile, extortion groups identified 455 legal entities on data leak websites, representing a 39 percent year-on-year increase.
“Law firms are the new ATM for cybercriminals. Adversaries are exploiting the value of privileged client information, and they're willing to go beyond the keyboard to get it,” CrowdStrike head of counter adversary operations Adam Meyers said in a press statement.
Identity-based attacks
The report also identified identity-based attacks targeting trusted access to cloud software, alongside espionage operations involving compromised billing systems and stolen credentials.
These tactics highlight potential risks for Southeast Asian legal practices as they increasingly rely on digital platforms to manage client records and transactions.
CrowdStrike emphasized the need for stronger visibility across user identities, devices, and cloud environments to detect intrusions before they escalate into extortion. —Vanessa Hidalgo | Ed: Corrie S. Narisma